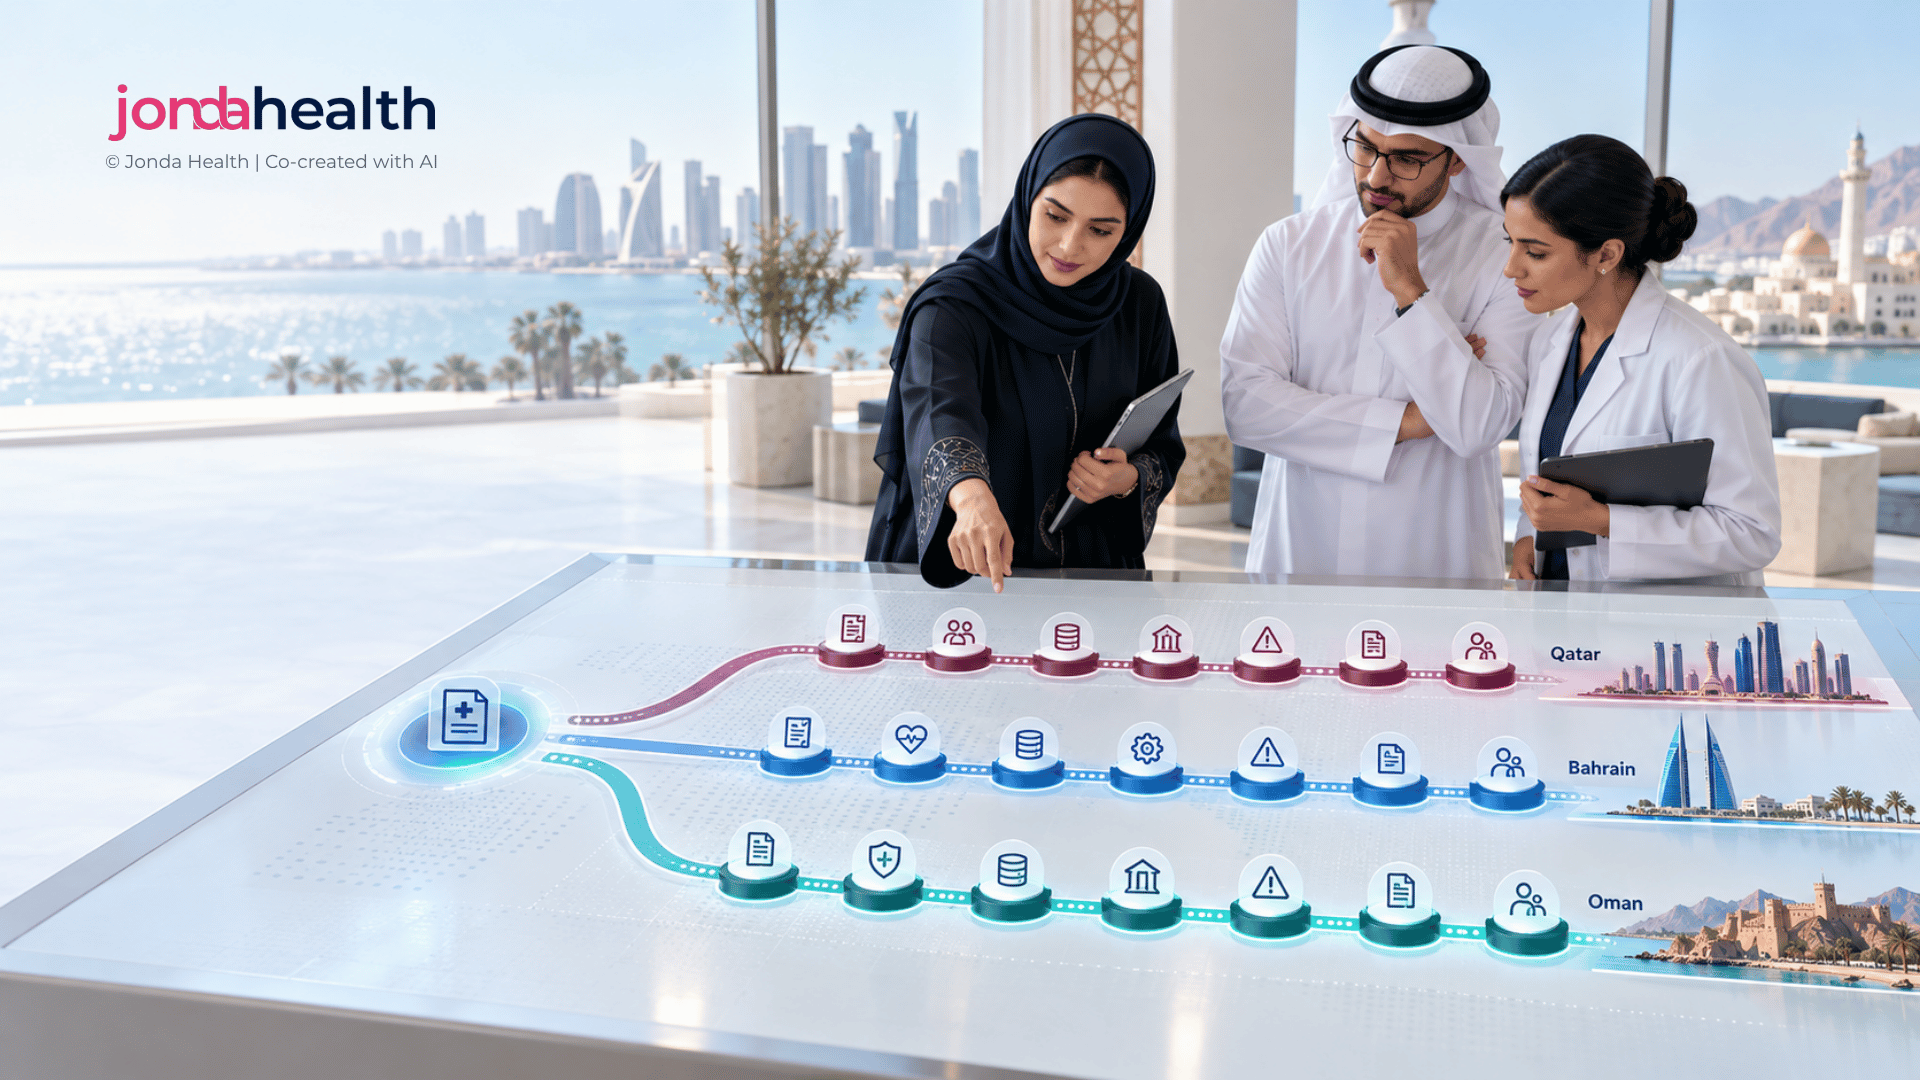
Three neighbouring countries, three different rulebooks for health data. If you provide care, build health technology or process clinical data across the Gulf, here is what changes as you cross each border.
The Gulf is often discussed as one market, and for many health technology companies it is one sales region. For health data, it is not. Each country has its own data protection law, its own regulator, its own approach to data leaving the country and its own national health record. A product or process that is compliant in one capital can need changes in the next.
This tracker compares Qatar, Bahrain and Oman across five things that most affect providers, insurers and health technology companies. It complements our articles on the UAE's health information exchanges and on Saudi Arabia's NPHIES. Rules change, so we note when it was last checked.
Last checked: October 2026. This tracker summarises published laws and guidance and is not legal advice.
Figure 1. The tracker at a glance. Details and sources for each row follow below.
Qatar. Law No. 13 of 2016 on Protecting Personal Data Privacy has applied since 2017, supported by guidelines issued in 2021. Entities in the Qatar Financial Centre follow separate QFC Data Protection Regulations.1 Health-sector rules from the Ministry of Public Health (MoPH) sit on top, including a 2022 directive on health insurance data.2
Bahrain. The Personal Data Protection Law, Law No. 30 of 2018, has applied since 1 August 2019. The Ministry of Justice, Islamic Affairs and Waqf acts as the data protection authority.3,4 A package of ministerial resolutions issued in March 2022 filled in the detail on transfers, security, sensitive data and breaches.5
Oman. The Personal Data Protection Law, Royal Decree 6/2022, took effect on 13 February 2023,6 with Executive Regulations issued in 2024. The transition period ended on 5 February 2026, so the law is now fully enforced. The Ministry of Transport, Communications and Information Technology (MTCIT) is the regulator.7
All three countries treat health data as specially protected. What they ask for before it is processed is different.
Qatar requires prior permission from the competent authority to process personal data of a "special nature", which includes physical and mental health (Article 16).1
Bahrain classes health data as sensitive and generally requires explicit consent, but allows processing without consent where it is needed for preventive medicine, diagnosis, the provision of care or treatment, or managing health services, when carried out by a licensed medical professional or someone bound by confidentiality.3 Automated processing of sensitive data needs prior authorisation from the authority.4
Oman generally prohibits processing health, genetic and biometric data without a permit from MTCIT.6
Figure 2. Three approaches to the same question. Summarised from the sources below.
Qatar's general law says controllers should not limit cross-border data flows unless processing breaches the law or could cause serious harm (Article 15), and the national Cloud Policy Framework of 2022 states that data residency is no longer a general requirement.1 Health insurance is the exception that matters most. The MoPH directive on national health insurance data requires it to be stored and processed on systems "hosted inside the state of Qatar", and prohibits transferring it outside the country. The same directive names HL7 FHIR as the national standard for exchanging health information.2
Bahrain allows transfers to countries on the authority's approved list without further authorisation. The list, set up in 2022, includes the UAE, Saudi Arabia, Oman, Jordan, Kuwait, Egypt, India, EU countries, the United Kingdom and the United States. Transfers elsewhere need authorisation or an exception such as explicit consent, and intra-group transfers can rely on approved corporate rules.5 Unlawful transfers are a criminal offence.3
Oman requires the data subject's explicit consent for transfers, and the receiving jurisdiction must offer protection equivalent to Oman's law. Transfers of sensitive data may also need approval from the national Cyber Defence Centre.7
Qatar has named HL7 FHIR as its national standard for exchanging health information, and plans for a national exchange hub (QHIE-Hub) to become the single gateway for patient health information exchange with the Ministry in future phases.2
Bahrain's Ministry of Health leads I-SEHA, the national health information system, through which professionals can view patient records and histories in real time and patients can manage their own information online. The government also describes a planned Digital Health Integration System for unified health data sharing.8
Oman runs the Al Shifa system across most public institutions. A 2025 study in the Eastern Mediterranean Health Journal, based on a survey of 250 institutions, found that digital systems support over 85% of Oman's healthcare institutions, but that there is no unified data exchange across institutions, that exchanging data between Al Shifa and private providers is a major difficulty, and that only a small proportion of institutions use international standards such as ICD-10.9
Figure 3. Selected findings from Al Salmi et al., Eastern Mediterranean Health Journal, 2025 (survey of 250 Omani institutions).
The pattern across all three is familiar from the rest of the region: strong national systems in the public sector, and a gap where private providers, outside records and unstructured documents meet them. That gap is where data quality, coding and identity matter most.
Bahrain requires controllers to notify the authority within 72 hours of becoming aware of a breach, unless it is unlikely to affect data subjects' rights, and to notify affected individuals where the risk is high.4,5 Criminal penalties for offences such as unlawful processing of sensitive data or unlawful transfers include imprisonment of up to one year and/or fines of BHD 1,000 to BHD 20,000.3
Oman requires notification to the regulator within 72 hours of a breach that may put data subjects' rights at risk, and to affected individuals within 72 hours where serious harm is likely.7 Fines for unlawful transfers outside Oman can reach OMR 500,000.6
Qatar requires serious breaches to be reported to the regulator, and affected individuals to be notified where there is significant risk, without a fixed statutory deadline. The regulator can impose administrative fines, and deliberate misconduct can lead to criminal proceedings.1
Three practical lessons stand out. First, there is no single "GCC compliant" setting: permissions, transfer rules and breach timelines need to be checked country by country, and a 72-hour breach process should be the default. Second, where data is processed and who can access it, including remote reviewers and support staff, is the question every regulator cares about. Third, the national records in all three countries are only as useful as the data flowing into them, which puts structured, coded and well-identified data at the centre of every compliance and interoperability effort.
Yes. Qatar requires prior permission to process health data, Bahrain classes it as sensitive personal data with a healthcare exception to consent, and Oman requires a permit from the Ministry of Transport, Communications and Information Technology.
Qatar's general data protection law does not impose a blanket localisation rule, but the Ministry of Public Health requires health insurance data to be stored and processed inside Qatar and prohibits transferring it abroad.
Bahrain keeps an approved list of countries with adequate protection, set up in 2022, which includes the UAE, Saudi Arabia, Oman, Jordan, Kuwait, Egypt, India, EU countries, the United Kingdom and the United States. Transfers elsewhere need authorisation or an exception.
Oman's Personal Data Protection Law took effect on 13 February 2023, and its transition period ended on 5 February 2026.
Bahrain and Oman require notification to the regulator within 72 hours. Qatar requires serious breaches to be reported without a fixed statutory deadline.
Working across the Gulf means meeting different rules with the same high standard of data. There are two ways we can support you.
Last checked October 2026. This tracker is for general information and is not legal advice; confirm current requirements with qualified advisers in each country.
Suhina Singh is a physician, the Founder and CEO of Jonda Health, and a health data strategist working at the intersection of artificial intelligence and clinical information systems.